NSA and Apple blame maintenance and an internal update for Tuesday outages; Equinor confirms a separate cyberattack that did not hit production
NSA and Apple said Tuesday’s outages came from maintenance and an internal update, not attacks. Equinor separately confirmed a cyberattack that spared production. A coordination narrative is speculation; the FBI’s ARTEX warning and FEMA’s scheduled alert test are real but not evidence those three events were one operation.
Documented: On Tuesday, November 17, 2026, the National Security Agency said it experienced a temporary degradation during scheduled routine maintenance. CNN, citing six people familiar with the matter, reported that NSANet, the agency’s classified internal communications network, was down and that the agency had staggered staff arrivals at Fort Meade. Those sources, and a White House spokesperson speaking on Newsmax, said there was no evidence of a cyberattack. The New York Times reported that an employee information line described a “code yellow,” the second-highest of three levels, and told non-emergency staff to delay arrival. The Wall Street Journal, citing a person familiar with the incident, attributed the interruption to a software update meant to patch the system. The NSA said some internal systems were affected but that mission-critical capabilities remained fully operational.
Documented, and separately: Apple told Bloomberg the same day that an internal update, not a cyberattack, caused outages affecting iCloud sign-in, the App Store, Apple Music, and related services, and that many systems were coming back. Equinor, in its own statement and as reported by Reuters and NRK, said it had detected an ongoing cyberattack against some IT systems, had informed authorities, and was working to neutralize it. The company said there was no indication data had been stolen and that operations and production were unaffected. Employees might see disruptions to some services.
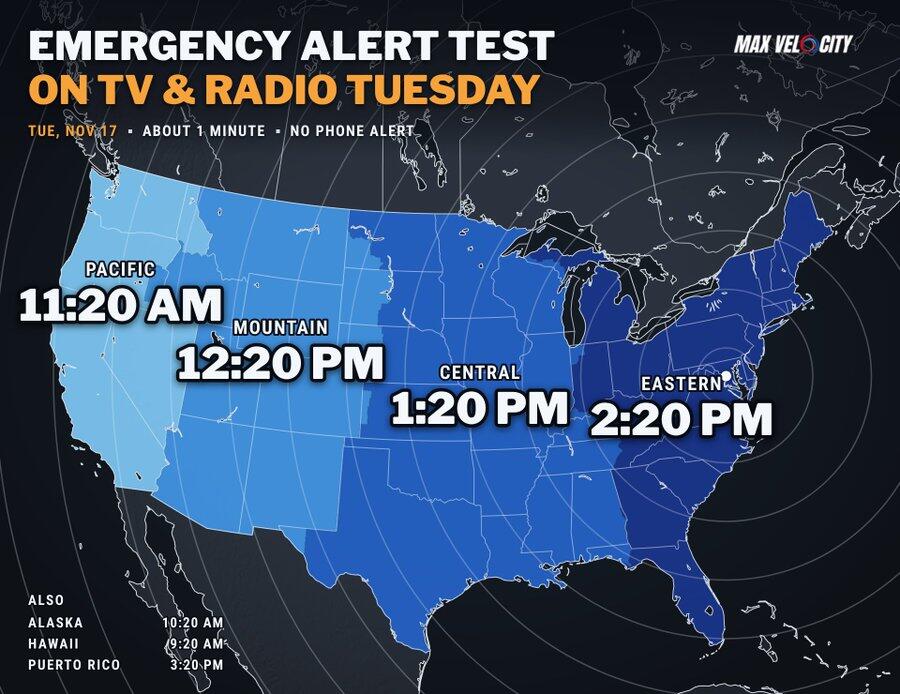
Documented, and not the same event: The FBI on November 13 published FLASH-20261113-001 warning that criminal and state-aligned actors have weaponized ARTEX, an open-source LLM-driven penetration-testing framework, to speed intrusions, including a ConnectWise-related supply-chain case involving attempted access to more than 2,250 downstream tenants. That advisory does not name NSANet, Apple, or Equinor. FEMA’s nationwide Emergency Alert System test, scheduled for about 2:20 p.m. Eastern on November 17 and announced weeks earlier by FEMA and the FCC, is a statutory drill, not an emergency response to these incidents.
Claimed: ZeroHedge and some cable commentary treated the day’s pile-up—NSA, Apple, Equinor, plus earlier Microsoft 365, FAA, and bank disruptions—as suspiciously simultaneous and possibly coordinated. A National Security Institute fellow, Mike Nelson, told NewsNation the NSA outage could have been an attack. That is an outside possibility, not an official finding.
Speculated, and not supported by the record available so far: that these events are a single state-aligned campaign against the surveillance state and critical infrastructure, or that the EAS test was cover for that campaign. What is documented is narrower and less cinematic. Two of the three headline disruptions were attributed by the organizations themselves to maintenance or an internal update, with officials saying they saw no cyberattack. The one confirmed intrusion, at Equinor, is real and was disclosed by the company, but it did not, on the company’s account, reach production. The interesting anomaly is not a proven hybrid-war strike. It is how often large, supposedly redundant systems fail under their own changes—and how quickly a coincidence of failures, a real energy-sector intrusion, and a standing FBI warning about automated intrusions get read as one plot.
People who depend on NSA analysis pipelines, Apple account services, and Norwegian energy IT saw real disruptions on the same day, but only Equinor has confirmed an intrusion, and it says production held. Treating every outage as one attack obscures both the confirmed energy-sector incident and the ordinary fragility of large software changes.
Sources (8)
- [1]CNN: Highly classified US national security communications network goes down(https://www.cnn.com/2026/11/17/politics/highly-classified-national-security-communications-network-goes-down)
- [2]The Guardian: NSA network for internal communications goes down(https://www.theguardian.com/us-news/2026/nov/17/nsa-national-security-classified-communications-network-down)
- [3]Reuters: Equinor detects ongoing cyberattack, output unaffected(https://www.reuters.com/technology/equinor-detects-ongoing-cyberattack-output-unaffected-2026-11-17/)
- [4]Equinor: Har avdekket cyberangrep(https://www.equinor.com/no/nyheter/20261711-equinor-har-avdekket-cyberangrep)
- [5]TechCrunch: Apple services hit by outage(https://techcrunch.com/2026/11/17/apple-services-including-icloud-app-store-and-apple-music-hit-by-outage/)
- [6]MacRumors: Apple blames internal update, says it was not a cyberattack(https://www.macrumors.com/2026/11/17/apple-outage-internal-update/)
- [7]FBI FLASH-20261113-001: Threat Overview of ARTEX(https://www.ic3.gov/CSA/2026/261113.pdf)
- [8]FEMA: 2026 Nationwide Emergency Alert System Test(https://www.fema.gov/emergency-managers/practitioners/integrated-public-alert-warning-system/national-test-2026)