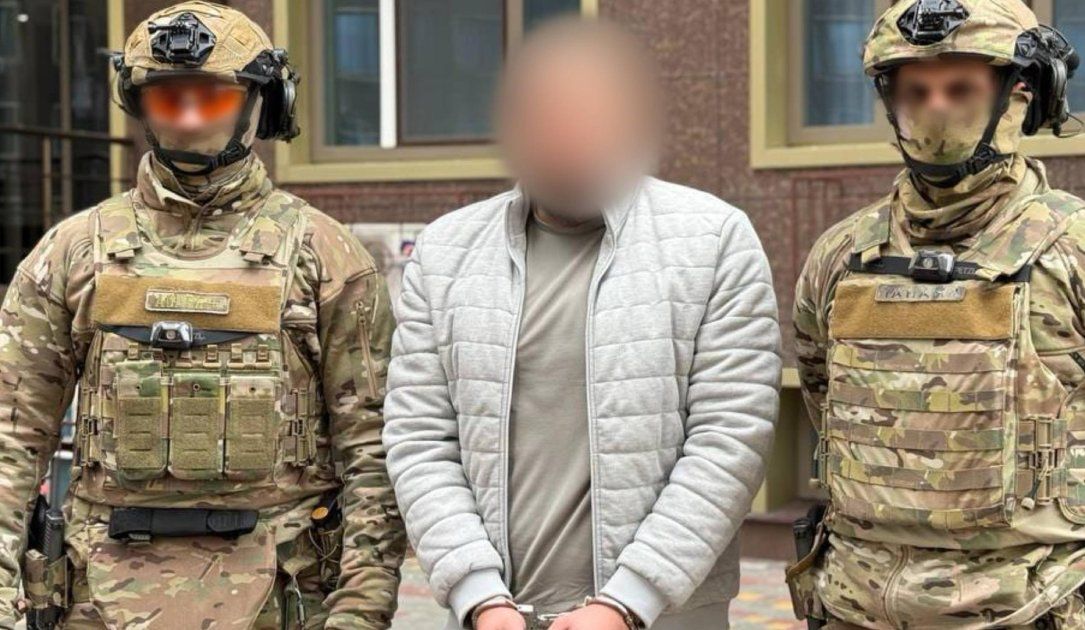
Ukraine arrests four in ransomware network that extorted $40.5 million from US oil and healthcare firms
Ukrainian authorities arrested four suspected key members of a Conti-linked ransomware network accused of extorting $40.5 million from at least 28 companies, including U.S. oil and healthcare firms. The case shows how social engineering and stolen credentials enabled large ransom payments across critical sectors.
Ukrainian police, working with U.S. law enforcement, arrested four suspected key members of an international ransomware organization after 66 coordinated searches in Kyiv and 11 regions. The Prosecutor General's Office said the group had at least 27 members from Ukraine, Russia and Kazakhstan and was tied to a wider network of more than 60 people across eight jurisdictions, including former Conti members. Investigators seized computers, phones, bank cards, about $370,000 in cash and 20,000 euros.
Court records reviewed by Recorded Future News identify alleged victims including Warren Oil Company, Maxxis International-USA, Newpark Resources and Quantum Health. The records allege Warren Oil paid about $5 million in bitcoin after attackers stole 1.4 terabytes in August 2024; Newpark paid $1.5 million after a $10 million demand; Quantum Health paid $5 million after a $15 million demand. One suspect allegedly used social engineering, posing as technical support to obtain credentials, while the group used Rocket.Chat, qTOX and Telegram.
The records describe a layered criminal structure with leaders, coordinators, social engineering specialists, technical operators and payment handlers, recruiting through underground forums. That pattern matters because it shows ransomware-as-a-service economics persisting after Conti: specialized labor, encrypted messaging and servers outside Ukraine. The operation also reveals how much of the damage came from credential theft rather than exotic exploits. Three named U.S. companies had earlier acknowledged attacks, but their disclosures had not confirmed ransom payments.
The arrests hit a network accused of draining $40.5 million from at least 28 companies, with damages potentially higher. Victims span oil and gas, pharmaceuticals, manufacturing, logistics, finance and critical infrastructure, sectors where outages can ripple into fuel supply, patient care and shipping. For U.S. businesses, the case underscores that help-desk calls and stolen passwords remain a primary intrusion route. For Ukraine and the FBI, it is a concrete disruption of a Conti-linked network still generating real revenue.
U.S. oil, healthcare, manufacturing and logistics firms are exposed because attackers gained access through credential theft, then extorted millions; the arrests show law enforcement can disrupt these networks but also reveal how widespread the damage already was.
Sources (1)
- [1]Original source(https://therecord.media/ukraine-ransomware-arrests-cyber)