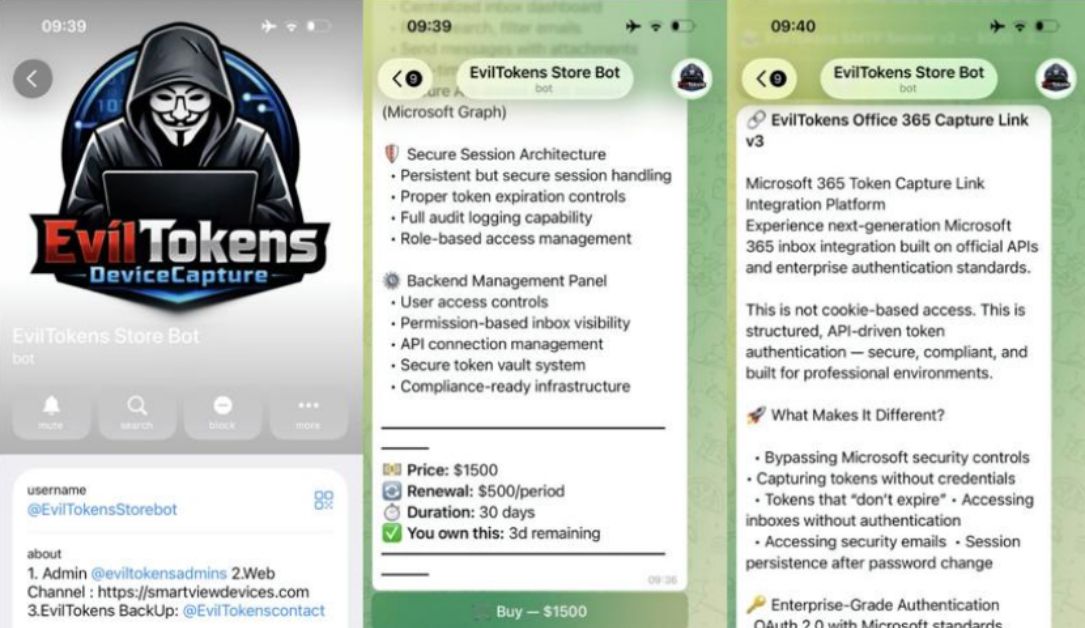
Microsoft Seizes EvilTokens AI Infrastructure, Triggers UK Arrests Over 12,000 Compromised Inboxes
Microsoft's disruption of EvilTokens reveals AI systems that move beyond phishing copy to full workflow automation including victim selection and monetization planning. The case highlights coordination between private sector legal action and UK law enforcement but leaves hosting and payment infrastructure details unaddressed. Continued operation of copycat services indicates the model remains economically viable.
The takedown exposed an AI system that automated the full criminal workflow: inbox analysis, relationship mapping, fraud strategy selection, and generation of targeted impersonation messages. Launched February 2026, the service processed data from over 12,000 breached accounts across 10,000 organizations concentrated in five English-speaking nations plus India. Subscription pricing of $1,500 initiation plus $500 monthly placed it in the mid-tier professional criminal market rather than script-kiddie territory.
Microsoft's partnership with Health-ISAC and OpenAI allowed rapid identification of multiple underlying models feeding the chatbot. This mirrors earlier disruptions of automated BEC tools but adds a new layer: AI that recommends monetization paths based on victim email content rather than generic templates. The 44 email themes observed indicate systematic A/B testing of lures, a capability previously requiring human teams.
Independent technical reporting has not yet confirmed whether the platform incorporated fine-tuned open-source models alongside commercial APIs. Official statements emphasize OpenAI cooperation while remaining silent on infrastructure hosting locations and payment processors, leaving open questions about third-party enablers that sustained operations for at least eight months before Microsoft reported to UK police in August.
Next steps hinge on whether the two bailed suspects yield access logs or co-conspirator identities. Similar AI-driven services are already appearing on Telegram with altered branding, suggesting rapid reconstitution unless payment rails and model access are jointly targeted.
Metropolitan Police: At least one additional arrest of EvilTokens support personnel within 90 days based on seized logs.
Sources (3)
- [1]Primary Source(https://therecord.media/two-arrested-in-uk-after-microsoft-takedown-eviltokens)
- [2]Supporting Source(https://blogs.microsoft.com/microsoft-security/evil-tokens-disruption)
- [3]Supporting Source(https://www.met.police.uk/news/2024/oct/cybercrime-arrests)